
What Is Port Scanning: How Port Scan Attacks and Open Port Checks Work
Before your script finishes loading a login page, the target platform's risk engine often probes your IP address in the opposite direction. That return check takes about 40 milliseconds. Security gateways test a dozen standard ports to check whether your connection exposes an active proxy listener. Knowing what is port scanning helps solve two practical tasks at once: locking down your own servers against external reconnaissance, and selecting proxy infrastructure that does not expose gateway ports during counter-checks.
TL;DR: What is a port scan and why it matters for network operations
Layer 4 diagnostics: port scanning is the automated probing of logical transport sockets (numbered 0 to 65535) across TCP and UDP to identify active network services.
Three core endpoint states: a network port scanner classifies target sockets into open, closed, and filtered ports based on packet headers returned by the host or firewall.
Inbound anti-fraud probing: risk engines (IPQualityScore, ThreatMetrix, PerimeterX) run active probing against connecting IPs for open proxy port detection on SOCKS5 port 1080 and HTTP proxy ports 8080 and 3128.
Reputation impact: when open port detection finds exposed proxy listeners on an incoming IP, the Fraud Score climbs past 75-85 and triggers session resets.
Gateway isolation: LTE/5G channels behind Carrier-Grade NAT (CGNAT) and a dedicated static ISP proxy behind stateful NAT drop unsolicited inbound probes, returning 0 open ports.
Multi-region auditing (EASM): routing authorized checks through a rotating residential proxy pool across 195+ countries verifies firewall geo-rules without triggering rate limits on your office subnet.
What is a network port and how port scanning works step by step
If an IP address identifies a specific building on the network, a port on Layer 4 (the Transport Layer of the OSI model) acts as the office number inside that building. Every network application opens a socket - a combination of an IP address, a transport protocol, and a 16-bit integer from 0 to 65535. Without this number, the operating system cannot determine whether to pass an incoming packet to an Nginx web server, a PostgreSQL database, or an SSH daemon.
IANA divides the port address space into three ranges:
System ports (0-1023): reserved for core services such as 80 (HTTP), 443 (HTTPS), 22 (SSH), and 53 (DNS). On Linux, binding a process to these ports requires root privileges.
Registered ports (1024-49151): used by application services, databases (3306 MySQL, 5432 PostgreSQL), and proxy daemons. This range includes SOCKS5 port 1080 and HTTP proxy ports 8080 and 3128, along with alternative port 8443.
Dynamic or ephemeral ports (49152-65535): allocated temporarily by the client OS for outbound connections during an active session.
At the packet level, examining how port scanning works step by step starts with the standard TCP three-way handshake. The client sends a synchronization packet (SYN), the server confirms readiness with SYN-ACK, and the client completes the connection with an ACK packet.
During open port detection, a network port scanner reads the exact response from each target socket:
Open port: the target service listens on the port and replies with SYN-ACK (in TCP) or returns valid application data (in UDP).
Closed port: the packet reaches the server OS, but no active process is bound to that number. The kernel immediately returns a reset flag (RST) or an ICMP Port Unreachable message.
Filtered port: a packet filter enforcing stateful firewall rules silently drops the packet (DROP), causing a connection timeout on the sender side.
👉 Run a pre-flight IP Fraud Score check in CyberYozh App ($0.15 per request) to verify your IP reputation before launching automated workflows.
What is a port scan attack: Legitimate network audits vs. network reconnaissance
Nmap and Masscan send identical packets whether run by a system administrator or an external bot. The difference lies in authorization and purpose. During routine maintenance, teams run an authorized external attack surface check on their own subnets to spot forgotten Docker containers, exposed Redis instances (6379), or database ports (3306, 5432) left open after a configuration update.
Unauthorized network reconnaissance looks different. When a third-party node probes foreign infrastructure without permission to map entry points, security systems log a port scan attack. Examining what is a port scan attack and how it works shows two main probing vectors:
Horizontal scans (Port Sweeps): probing a single port (such as 22 for SSH or 3389 for RDP) across thousands of IP addresses within a subnet.
Vertical scans: checking a single target IP across all ports from 1 to 65535 to build a complete profile of running services.
It also helps to clarify the difference between port scanning and vulnerability scanning, as well as routine uptime monitoring. Minute-by-minute TCP monitoring only verifies whether a known service (such as port 443 on a payment gateway) is responding. Basic port scanning maps all accessible entry points and grabs service banners (Banner Grabbing). Vulnerability scanning follows next: a specialized analyzer compares detected software versions against CVE databases to test for known configuration flaws.
👉 Explore proxies for cyber threat intelligence in CyberYozh App to conduct authorized external perimeter audits.
Main types of port scanning techniques for TCP and UDP
Choosing among different types of port scanning depends on the target transport protocol and firewall configuration. Before probing ports, utilities often send an ICMP echo request (ping sweep) to check if the host is active, though many administrators block ping at the edge gateway. Comprehensive TCP and UDP port scanning combines several packet-crafting techniques.
Scan method (types of port scanning) | Sent packet / flags | Open port response (Open) | Closed port response (Closed) | Firewall filtered response (Filtered) | Operational behavior and IDS visibility |
TCP Connect Scan (Vanilla Scan) | Full TCP three-way handshake: SYN -> SYN-ACK -> ACK | Returns SYN-ACK, completes full connection | Returns reset packet RST | Connection timeout or ICMP Unreachable | Uses standard OS connect() system call without root access; logged by application services. |
TCP SYN Scan (SYN half-open scan) | Initial SYN packet only (nmap -sS) | Returns SYN-ACK, scanner immediately sends RST | Returns reset packet RST | Packet dropped (DROP) with no reply | SYN half-open scan requires root privileges for raw sockets; faster execution that avoids application-layer logs. |
UDP Scan | Empty or protocol-specific UDP datagram (DNS 53, QUIC 443) | Application UDP response (no response marked open|filtered) | ICMP Port Unreachable error (Type 3, Code 3) | Timeout or administrative ICMP prohibition | Connectionless protocol; slow scanning speed due to Linux kernel rate limits on ICMP error generation. |
TCP ACK Scan | Standalone ACK flag without prior session | Returns RST (labeled Unfiltered - packet reached host) | Returns RST (labeled Unfiltered) | No response (blocked by stateful firewall rules) | Does not detect open ports directly, but maps whether stateful firewall rules are active. |
FIN / NULL / XMAS Scans | Packets missing SYN: FIN only, zero flags, or FIN+URG+PSH | No response on RFC 793 compliant OS (Linux/BSD) | Returns reset packet RST | Timeout or ICMP unreachable error | Tests stateless packet filters; ineffective against Windows hosts, which return RST regardless of port state. |
In practice, combining TCP and UDP port scanning gives a complete view of the network perimeter. For example, if a server runs HTTP/3 over QUIC, checking only TCP sockets will miss active UDP port 443.
👉 Deploy IPv4/IPv6 datacenter proxies from CyberYozh App (from $1.77/month for Shared and $2.18/month for Dedicated) for high-speed HTTP and SOCKS5 infrastructure testing.
Why anti-fraud systems scan ports 1080, 3128, and 8080: Open proxy port detection
Port checks cut both ways. Beyond inbound server defense, they directly affect web automation, public data collection, and regional profile management through browser management tools.
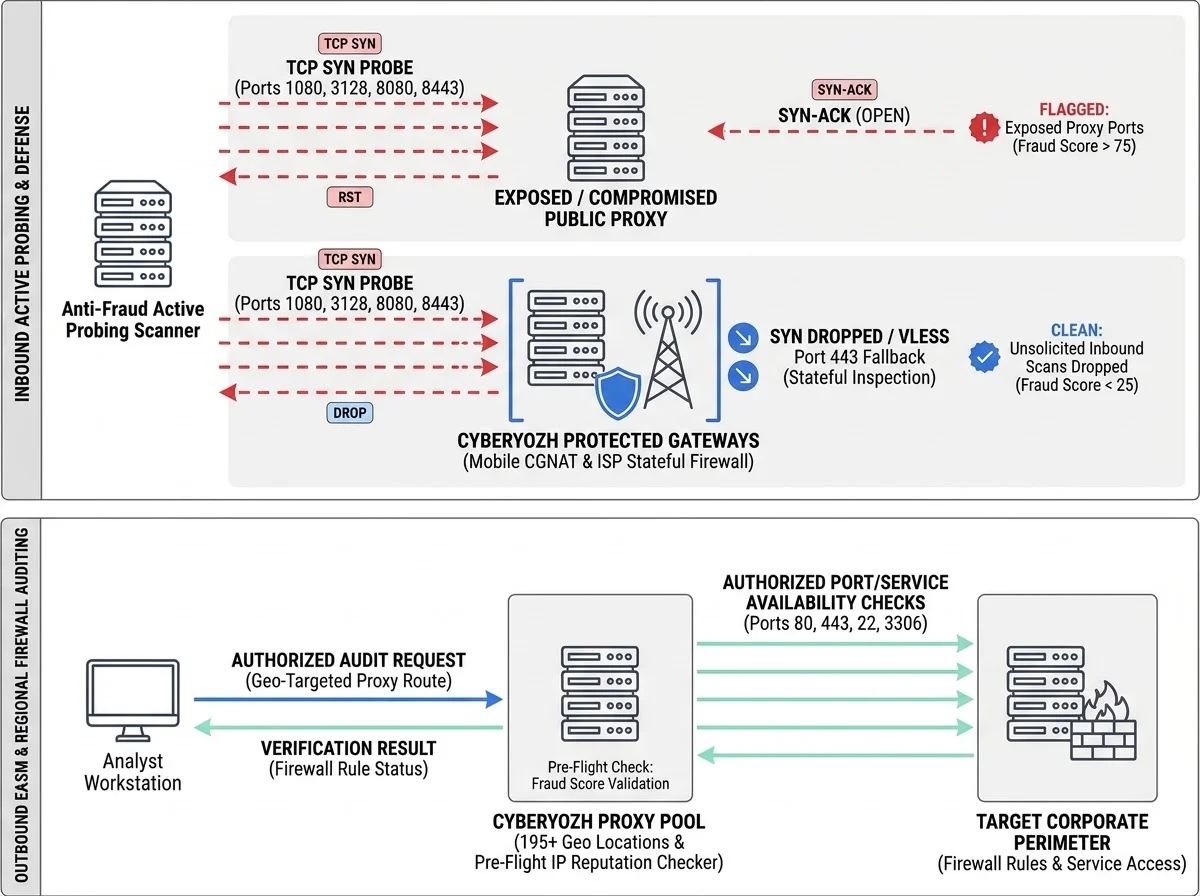
When a browser profile or script connects to a target site, risk engines (IPQualityScore, ThreatMetrix, PerimeterX, MaxMind) do more than check the Autonomous System Number (ASN). Security gateways immediately run active probing against your connecting IP address to check common active probing ports. Why anti-fraud systems scan ports 1080, 3128, and 8080 first:
Port 1080: the standard interface for SOCKS4 and SOCKS5 protocols under RFC 1928.
Port 3128: the default port for the Squid caching proxy, often opened by botnets on compromised home devices.
Ports 8080, 8000, 8888, and 8443: common alternative ports for HTTP/HTTPS proxying via the HTTP CONNECT method.
Under normal conditions, a home router or cellular smartphone exposes no inbound services. Home routers operate behind stateful NAT, while mobile carriers route traffic through Carrier-Grade NAT (CGNAT) gateways (RFC 6598, subnet 100.64.0.0/10). Any unsolicited inbound SYN packet from an anti-fraud scanner is dropped at the carrier gateway because no matching outbound session exists in the translation table.
Servers from public proxy lists, unconfigured VPS instances, or home routers with active UPnP and forgotten port forwarding rules behave differently. On those hosts, open proxy port detection finds exposed SOCKS5 port 1080 and HTTP proxy ports 8080 or 3128, or receives a predictable protocol handshake.
That directly shows how open proxy ports affect IP reputation and Fraud Score. When a node also generates network noise, its Abuse Velocity metric (the frequency of complaints and suspicious requests over a short window) rises, pushing the Fraud Score above 75-85. That is why public or unscreened proxy IPs get reset right on the login page.
In CyberYozh App, this open ports risk during counter-probing is resolved at the network architecture level:
LTE/5G Mobile Proxies (from $1.70/day for Shared and $3.50/day for Dedicated channels with unlimited traffic): traffic runs through physical modems and SIM cards on real mobile carrier networks where Carrier-Grade NAT (CGNAT) drops inbound probes. Dedicated mobile channels also support passive OS fingerprint (p0f) alignment (matching Windows, macOS, or Android profiles) and VLESS with XTLS-Reality transport on port 443. If an external scanner probes port 443 without a valid UUID, the node transparently redirects the request to a donor domain.
Static residential ISP proxies and rotating pools: before entering the active pool, nodes pass through Advanced IP Filtering to exclude addresses with open service ports.
👉 Switch to CyberYozh App LTE/5G mobile proxies with unlimited traffic (from $1.70/day) to route workflows through real carrier CGNAT networks with VLESS support.
Using proxies for external network availability testing and selecting the right proxy type
The second operational intersection between port checks and proxy infrastructure involves External Attack-Surface Management (EASM), compliance auditing, and localized QA testing. When security and DevOps teams run an external attack surface check from a single corporate office IP, they quickly hit two blind spots:
Their own Web Application Firewall (WAF) or Intrusion Prevention System (IPS) triggers rate limiting or temporary IP blocks against the office subnet after a burst of connection attempts.
Regional ISP filtering and geo-specific firewall rules remain invisible from headquarters - an enterprise firewall might block port 22 or 8443 in Europe while accidentally leaving it accessible to traffic originating from North America or Asia.
Using proxies for external network availability testing shows how services respond to users in the US, Germany, Japan, or Brazil while isolating your corporate lab from external counter-scanning.
When checking TCP ports through a proxy gateway, protocol mechanics matter: standard SOCKS5 CONNECT forwards payload data only after the proxy server completes a full TCP three-way handshake with the target host. While you cannot send raw single packets for a half-open scan through a proxy, you can run full TCP socket availability checks from the target location using curl, nc (netcat), nmap -sT with proxychains4, or Python scripts.
Example CLI commands for verifying regional port accessibility through a CyberYozh App SOCKS5 gateway:
# Test regional availability of port 443 and custom port 8443 via SOCKS5 proxy

curl -v --socks5-hostname user:password@gw.cyberyozh.com:1080 https://your-target-domain.com:8443 --connect-timeout 5

# Run an authorized TCP Connect check (-sT) without prior ping (-Pn) via proxychains4

proxychains4 nmap -sT -Pn -p 22,80,443,3306,5432,8080 your-target-domain.com
For automated availability auditing and public web data collection at scale, engineering teams can also integrate open-source tools Yozh Scraper and Yozh Crawler (MIT license, native MCP server support for AI agents, exporting to JSON, CSV, Parquet, and Excel), which route requests directly through CyberYozh App proxy pools.
Matching CyberYozh App proxy infrastructure to your workflow
Selecting the right proxy depends on whether you need long-term use of a single IP, broad regional coverage, or high platform trust:
Dedicated static ISP proxy (from $5.29/month): a dedicated static IP from a real broadband provider with unlimited traffic, 99.9% uptime, and HTTP/SOCKS5 support. Fits continuous server availability monitoring, allowlisting a test IP on staging firewalls, and long-running sessions.
Rotating residential proxy pool (usage-based billing per GB, starting from $4/GB with a 3 GB minimum package down to $2.50/GB at 100 GB): provides access to 100M+ residential IPs across 195+ countries. Features include 24-hour sticky sessions, Advanced IP Filtering, free geo-targeting, automatic traffic rollover to the next billing month, a Mass Credentials Generator, and full API access. This setup suits multi-country firewall verification, localized SERP tracking, and high-volume public web data collection.
Mobile LTE/5G proxies (from $1.70/day for Shared and $3.50/day for Dedicated channels): includes unlimited traffic, real cellular carrier connections, HTTP/SOCKS5/UDP support, VPN/VLESS configurations, and manual or API IP rotation. Best suited for trust-sensitive platforms, managing separate accounts per client, and search engine scraping (where mobile carrier IPs are harder for Google to flag and unlimited traffic supports multiple parallel threads).
Datacenter proxies IPv4/IPv6 (from $1.77/month for Shared and $2.18/month for Dedicated): offers unlimited traffic and low latency over HTTP and SOCKS5 for high-speed API testing and infrastructure diagnostics where residential ASN classification is not required.
👉 Configure a dedicated static ISP proxy (from $5.29/month with unlimited traffic) or connect to the rotating residential proxy pool across 195+ countries for multi-region availability testing.
How to protect network endpoints against port scan attacks and validate IP risk before execution
Effective perimeter defense works on two levels: configuring packet filters on your own hosts and checking client proxy reputation before launching traffic. Left unattended, open ports quickly escalate from software version leaks to brute-force attempts against SSH, databases, or admin panels.
Step-by-step practices for how to protect network endpoints against port scan attacks on Linux servers and enterprise gateways:
Enforce a default DROP policy in stateful firewall rules: returning a RST packet on closed ports immediately tells a scanner that your host is online and lets it sweep all 65,535 sockets in seconds. Configuring stateful firewall rules to silently DROP unsolicited packets forces the scanner to wait for connection timeouts on every probed port.
Bind internal services to localhost (127.0.0.1): databases (MySQL 3306, PostgreSQL 5432, Redis 6379) and internal APIs should never listen on 0.0.0.0 unless explicitly required.
Restrict administrative access and disable UPnP: lock down port 22 (SSH) to specific allowlisted IPs, and disable Universal Plug and Play (UPnP) on edge routers so local applications cannot open external ports automatically.
Deploy connection rate limiting and IDS/SIEM alerts: use nftables, iptables, Fail2ban, or Suricata to detect and block IP addresses that trigger abnormal bursts of SYN packets or hit multiple closed sockets within a short window.
Example Linux nftables configuration implementing stateful inspection and dropping invalid flag combinations:
table inet filter {

    chain input {

        type filter hook input priority 0; policy drop;


        # Allow packets belonging to established outbound sessions

        ct state established, related accept


        # Drop malformed packets used in NULL and XMAS port scans

        ct state invalid drop

        tcp flags & (fin|syn|rst|psh|ack|urg) == 0x0 drop

        tcp flags & (fin|psh|urg) == (fin|psh|urg) drop


        # Allow loopback and explicitly required public ports (e.g., HTTPS 443)

        iif "lo" accept

        tcp dport { 443 } ct state new accept

    }

}
The second step before launching automated scripts in Playwright, Puppeteer, Selenium, or Scrapy is pre-flight risk evaluation. Even when your own server is locked down, routing requests through an unverified external IP with a high Abuse Velocity metric triggers target blocks.
The built-in IP checker in CyberYozh App ($0.15 per check, or via the $19/month subscription covering 1,500 IP checks, 1,500 phone number checks, and 500 bank card checks) queries 5 anti-fraud engines and 118 OSINT blacklists. Running a pre-flight Fraud Score check verifies address cleanliness before sending the first request.
Reliable network operations rely on strict filtering rules and verifying addresses before running traffic. Packet filters protect your own servers against external probing, while isolating endpoints through CGNAT mobile networks, pre-screened residential ISP proxies, and pre-flight Fraud Score checks prevents anti-fraud blocks on outbound sessions.
👉 Check IP reputation before running traffic and explore proxy options by country inside the CyberYozh App platform.